RONIN BLOG
  • 🏠
  • COLLECTIONS
  • DOCS
  • SUPPORT
  • SLACK
  • RONIN LINK
  • RECENT NEWS
Sign in Subscribe
mfa

Creating New Users

Now you have your shiny new RONIN you need to fill it up with users.

  • Don Hancock

Don Hancock

18 Sep 2018 • 2 min read
Share
Creating New Users

Now you have your shiny new RONIN you need to fill it up with users.
👀
If RONIN has been connected to your institution identity provider, there is no need to follow these steps. Users will automatically be added to cognito once they login to RONIN for the first time with their institution credentials.

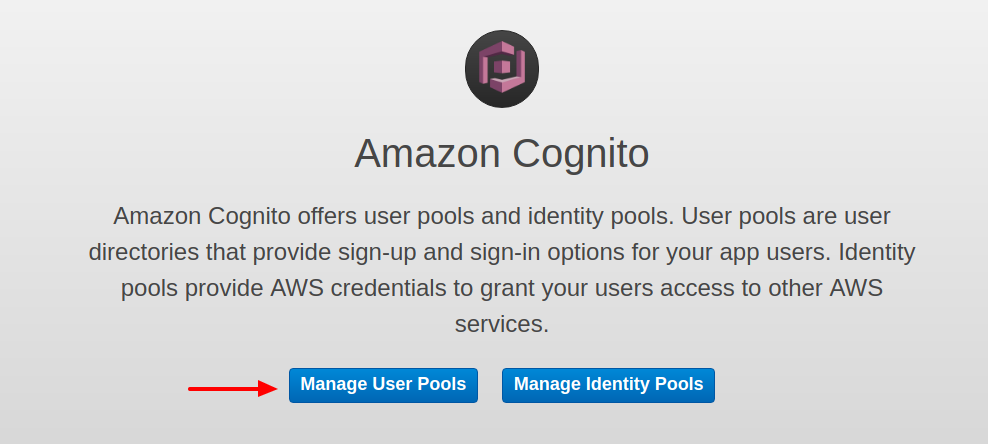
Step 1 - Login to your AWS account and head to Cognito.

Go to your AWS account that RONIN is install on and head to the cognito service and select "Manage User Pools".
Step 2 - Select your User Pool

Click on the user pool that ends in "-mfa".
Step 3 - Click "Create User"
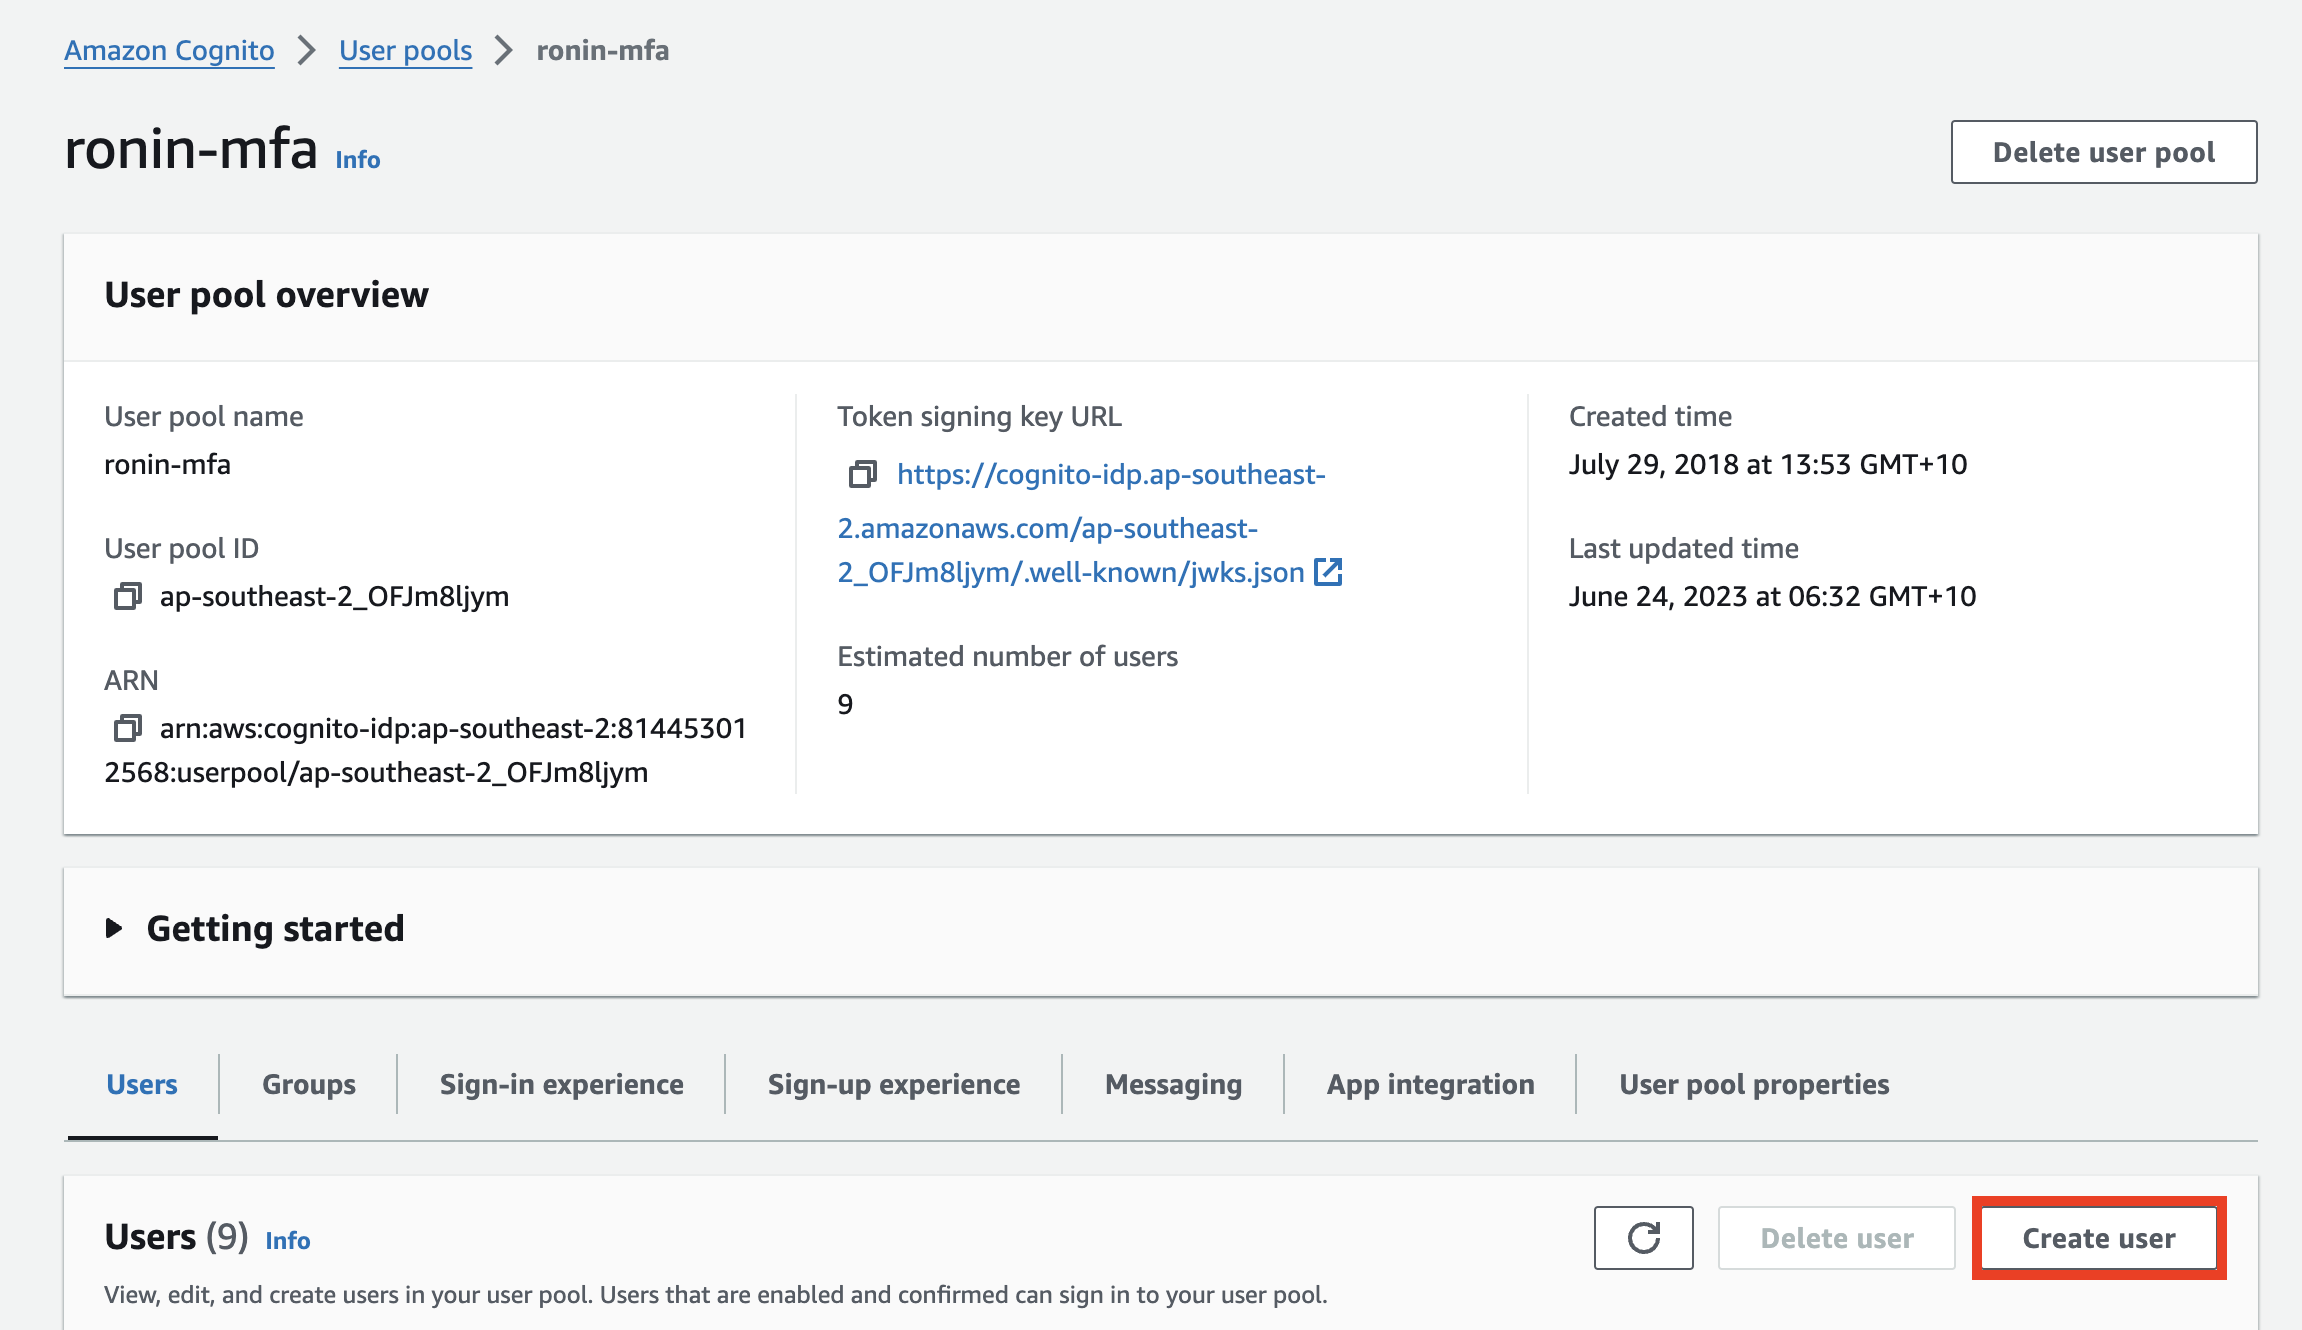
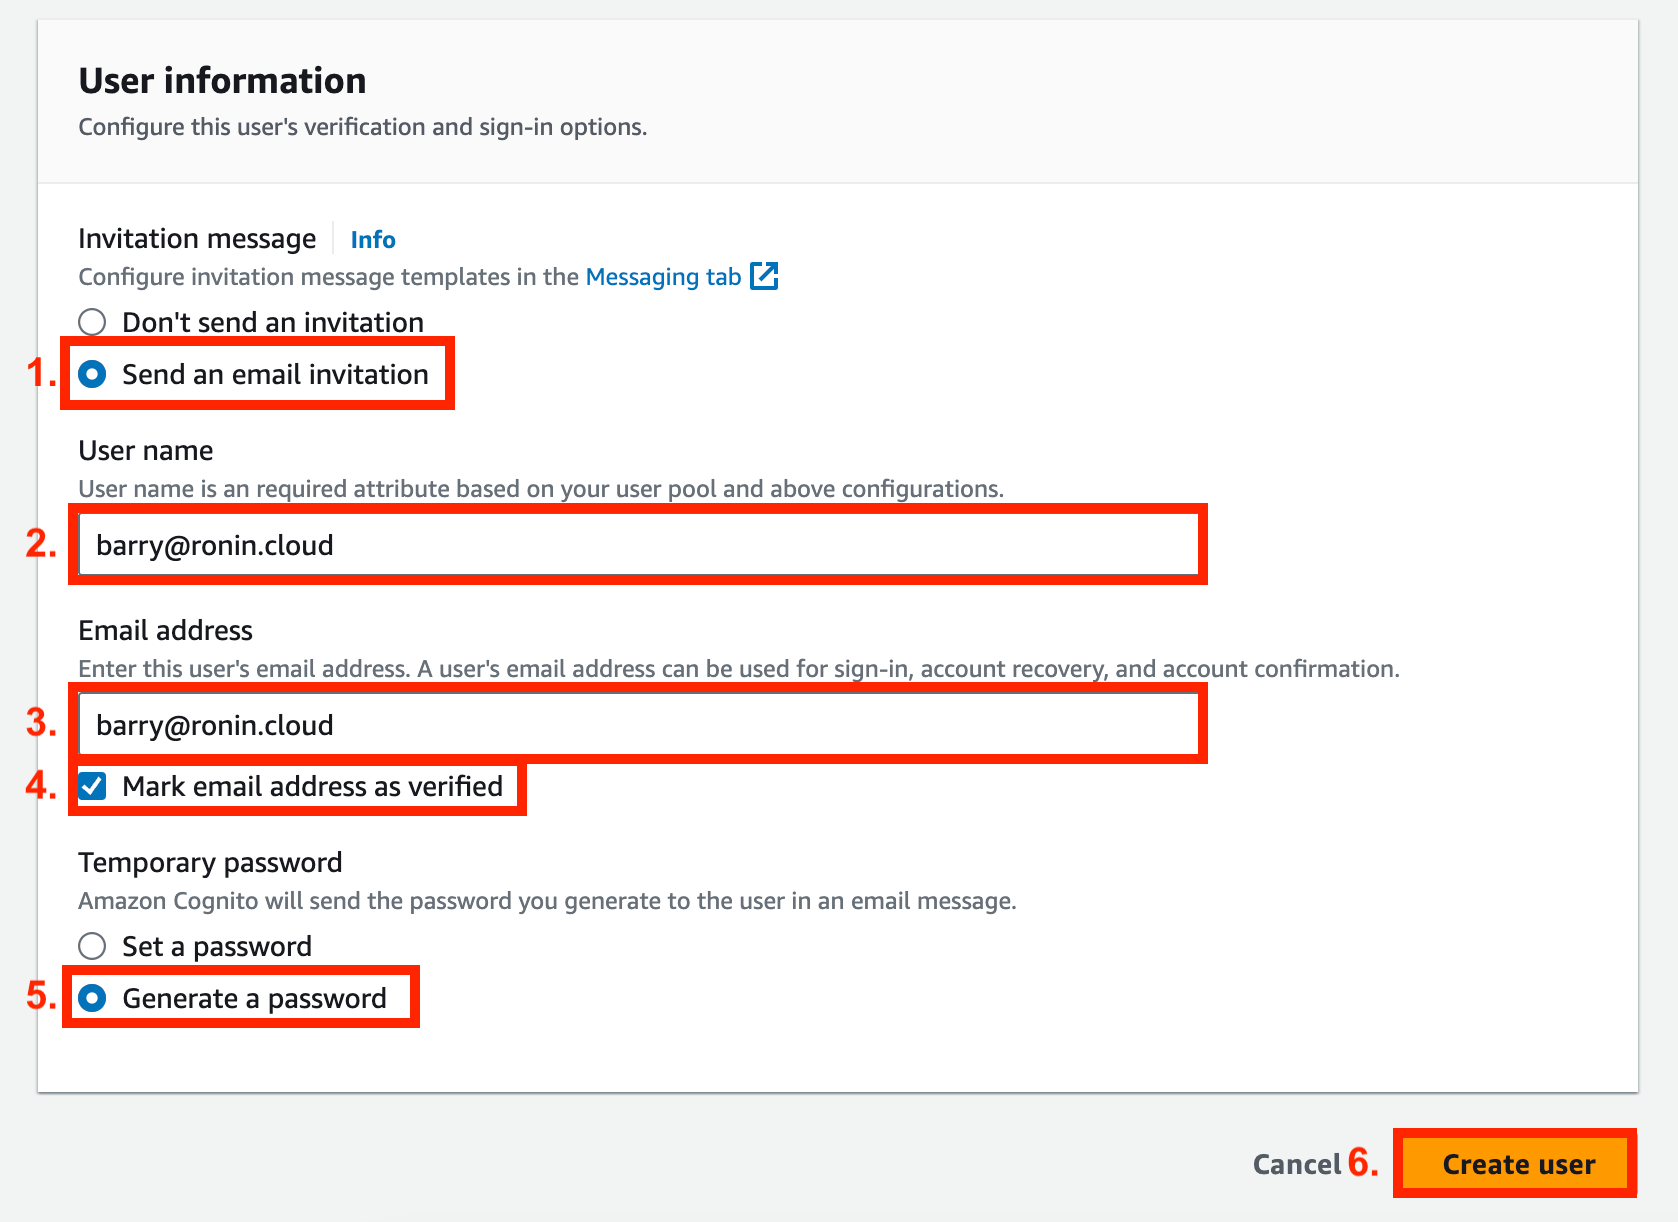
Fill in the form with the following information:

  1. Ensure "Send an email notification" is checked
  2. Set a username, we recommend this be the user's email address
  3. Enter the users email address
  4. Check "Mark email address is verified"
  5. Ensure "Generate a password" is checked
  6. Click "Create user"
✅
Hooray!! Barry should receive an email with his username and one time temporary password.

Step 4 - Make the user an administrator (optional).

Select your new user from the list of users by clicking on the username

Scroll down to the "Group memberships" section and click "Add to group"
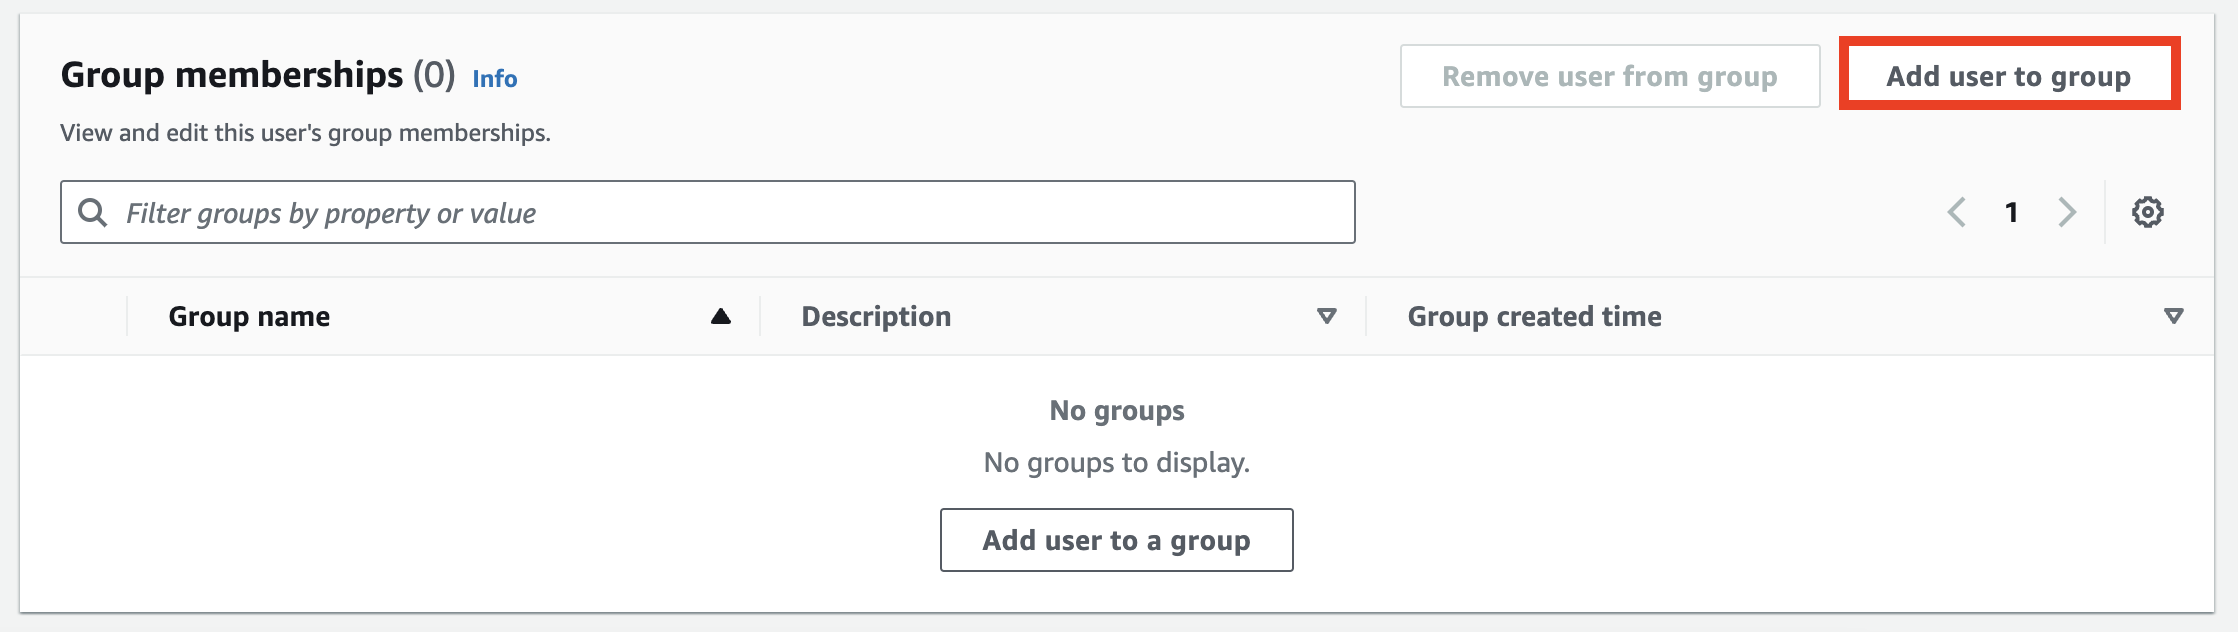
Add the user to the required admin group - see this blog post for more information.
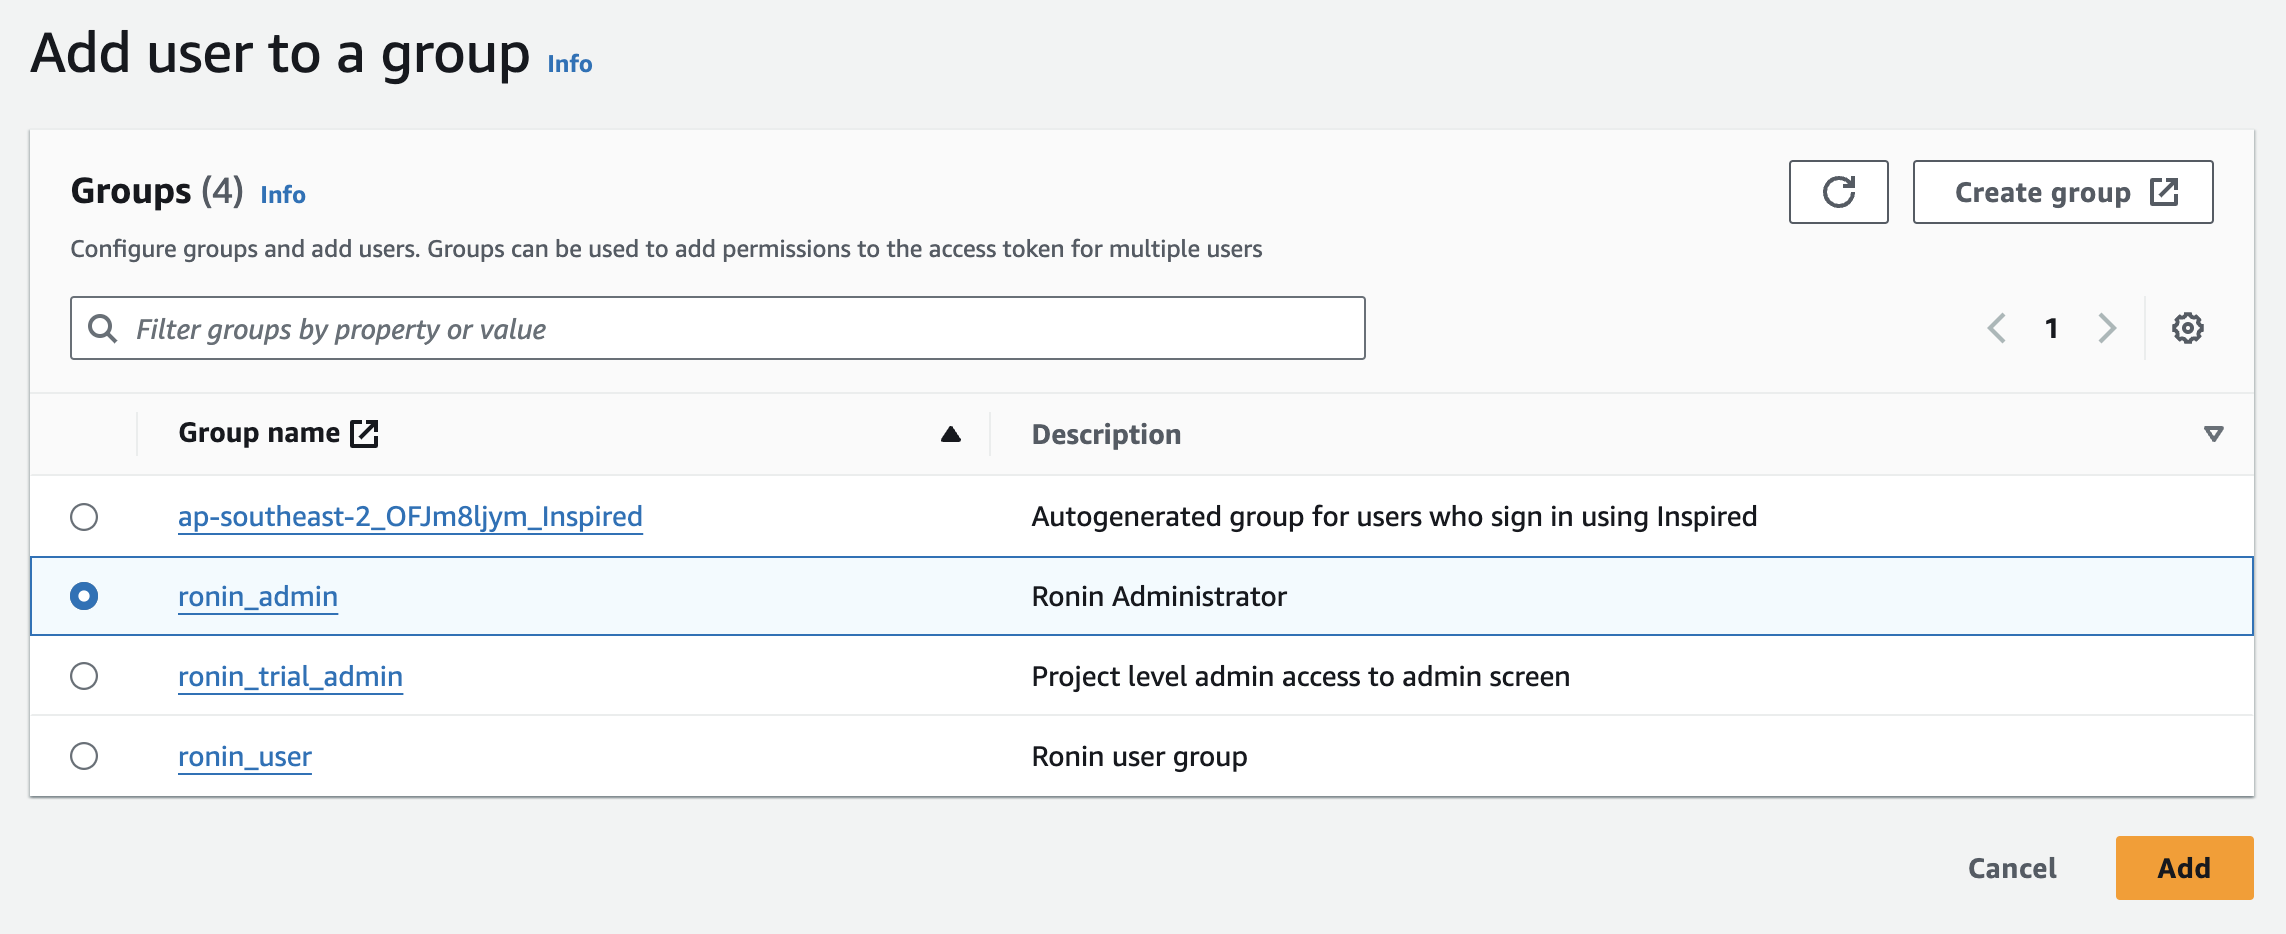
Note: Users automatically assume "ronin_user" permissions, so there is no need to add them to the ronin_user group. You can remove a user's Admin access at any time by removing them from an admin group.

✅
Nice work. We are done with Cognito now.

Step 5 - Add your new user to a RONIN project

Now Barry has access to RONIN we need to assign him to a project. For help with that go read this awesome blog.
Adding users to a project
Note. There were no Barrys' injured in the writing of this blog.

Sign up for more like this.

Enter your email
Subscribe
Don't Fear the Audit: Hold the Certificate From Day One

Don't Fear the Audit: Hold the Certificate From Day One

Build confidence before researchers log in. This guide explains how to create a clean RONIN Isolate environment, connect continuous compliance and security tools, complete an independent audit and apply proportionate controls across research workloads.
22 Oct 2026 5 min read
RONIN and the AWS Secure Research Environment: Better Together

RONIN and the AWS Secure Research Environment: Better Together

The AWS Secure Research Environment provides the governed cloud foundation; RONIN adds researcher self-service on top. Learn how they complement each other, support tiered compliance and give researchers access to compute, storage, apps and cost controls.
21 Oct 2026 5 min read
Beyond the Remote Desktop: What Researchers Actually Need From a Secure Environment

Beyond the Remote Desktop: What Researchers Actually Need From a Secure Environment

A secure remote desktop is a useful starting point, but researchers also need scalable compute, GPUs, storage, specialist apps and cost visibility. See how self-service within IT guardrails improves adoption and keeps research inside the secure environment.
20 Oct 2026 4 min read
RONIN BLOG © 2026
Powered by Ghost